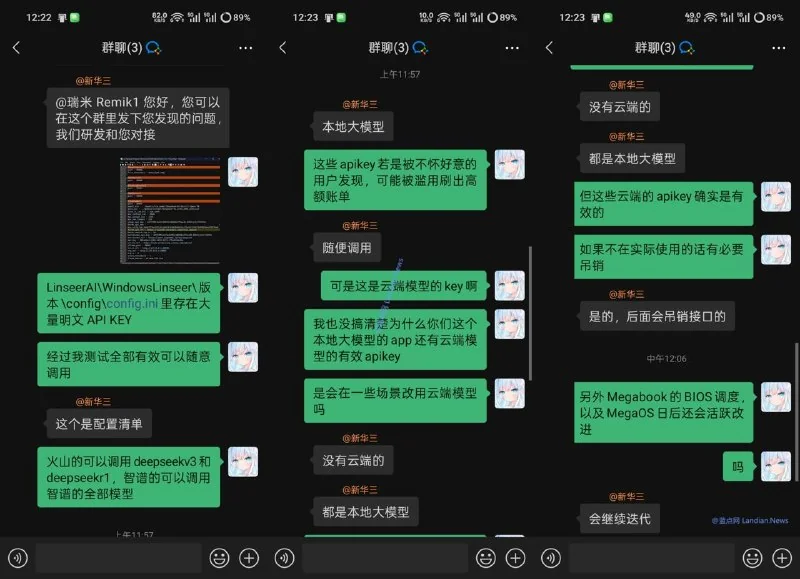
H3C's Lingxi AI assistant had a big problem: it claimed to run entirely on a local NPU, but its installer contained plaintext API credentials for multiple cloud-based large language models. The config file hardcoded valid keys for Zhipu AI, Baidu Qianfan, and ByteDance Volcengine.
A security researcher discovered the leak in late January and reported it to H3C. The company didn't revoke all the compromised credentials until early May—a full three months later.
That's an unusually long response time. Industry observers speculate that H3C may have had multiple internal teams sharing the same API keys, making it difficult to shut them down without a thorough audit. Fortunately, the product has a small user base, so attackers didn't have a chance to rack up massive bills.