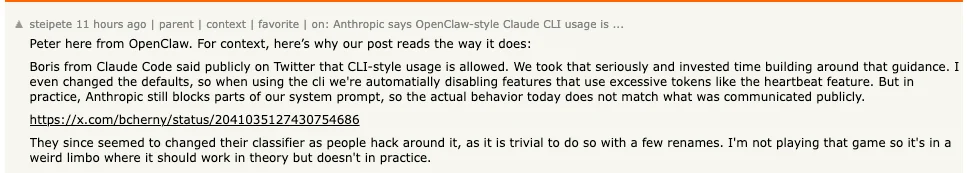
Someone screenshotted the line from OpenClaw's latest docs — "Anthropic permits OpenClaw-style Claude CLI usage" — and posted it to Hacker News. It hit the front page, then spread across X. OpenClaw founder Peter Steinberger responded on both platforms, giving the clearest picture yet: the verbal OK is real, and so is the actual block.
According to Steinberger, Claude Code lead Boris Cherny publicly stated on X that CLI usage is allowed. OpenClaw reinstated support based on that, disabling high-token-consumption features like heartbeat by default. But when the team tested it, Anthropic's servers were still fingerprinting and rejecting OpenClaw's system prompt fragments. Calls got blocked anyway. Steinberger added that a few renames would bypass the classifier — but he doesn't want to play whack-a-mole.
https://twitter.com/bcherny/status/2041035127430754686
Under the hood, OpenClaw connects to Claude Code by calling claude -p — the official Claude CLI's one-shot non-interactive mode. There's no separate bypass channel. Whether it uses an API key or a Pro / Max / Team subscription depends on which account the local Claude CLI is logged into. Anthropic's "ban on OpenClaw" isn't about blocking the claude -p command itself; it's a server-side system prompt fingerprint that flags and rejects OpenClaw. Boris's verbal "CLI allowed" and the docs' "claude -p reuse is tacitly permitted" refer to the same thing — the only gap between a subscription being able to run OpenClaw and actually working is whether the classifier lets it through.
OpenClaw removed Claude CLI from its default new-user onboarding in v2026.4.5, then added it back two days later in v2026.4.7 — along with a batch of environment variable cleanups and permission restrictions. The "re-allowed" language in the current docs corresponds to that v2026.4.7 change.