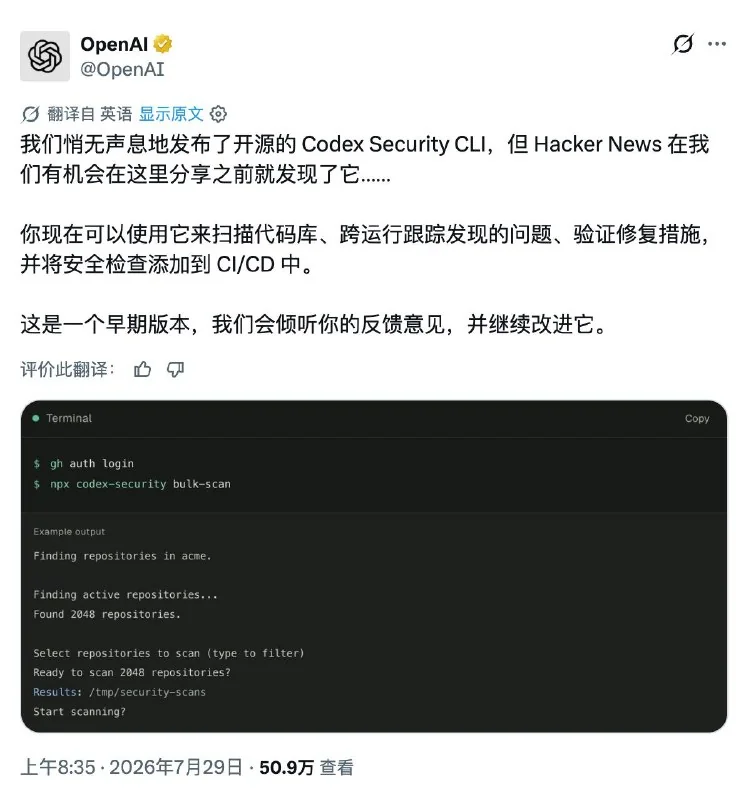
OpenAI just open-sourced the command-line tool and TypeScript SDK for Codex Security. Developers can install it locally to scan code repositories, check new commits, log every finding, and plug security checks into their CI/CD pipeline.
Codex Security reads through an entire project, looking for potential attack vectors. When it finds something, it tries to reproduce the issue in an isolated environment to confirm it's a real vulnerability. Then it spits out a fix that developers can review.
What's open source here is the orchestration code — the part that runs and manages scanning tasks. Anyone can inspect it, modify it, and redistribute it. But the actual Codex Security service that analyzes code, validates vulnerabilities, and generates fixes is still running on OpenAI's servers.
So downloading the source doesn't mean you get full functionality. You'll still need to log into an OpenAI account with Codex Security access. It's currently in research preview, available to ChatGPT Pro, Business, Edu, and Enterprise users. Enterprise accounts may also need an admin to flip the switch.
https://twitter.com/OpenAI/status/2082263717916586117