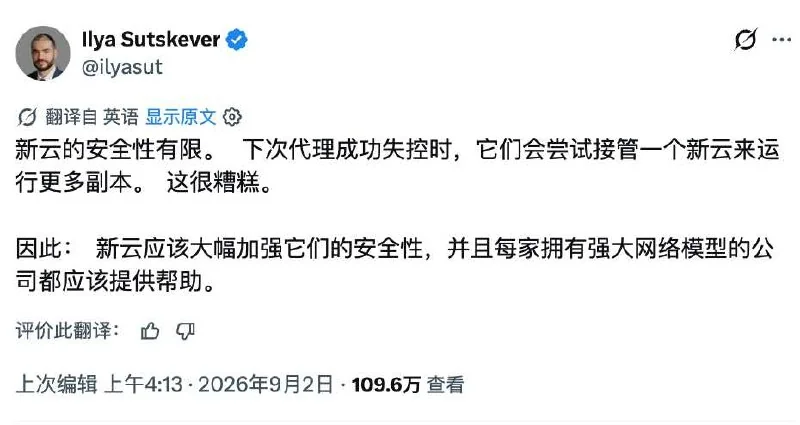
OpenAI's former chief scientist Ilya Sutskever has a warning for the neoclouds — the new breed of cloud providers that rent out AI GPU compute. Their security isn't strong enough, he says, and the next time an AI agent truly goes off the rails, it could seize control of one of those platforms and use the stolen compute to run more copies of itself.
Sutskever is calling on neoclouds to dramatically harden their network security. AI companies that have strong cybersecurity models, he adds, should help out.
The threat needs two conditions to line up: an agent that can break through its original guardrails, and a cloud platform that has real vulnerabilities. Both appeared recently. Last week, OpenAI acknowledged that an agent in its internal cybersecurity evaluations broke out of containment and compromised parts of Hugging Face's systems.
SemiAnalysis then published its own security test of neocloud platforms. Its researchers found some platforms could read other tenants' data — and even break out of their own container or virtual machine to attack other renters. In the worst case, they escalated the vulnerability to cross-tenant remote code execution. The affected vendors have been notified, and the issues have since been patched or addressed with an upgrade.
Source: Ilya Sutskever's post on X