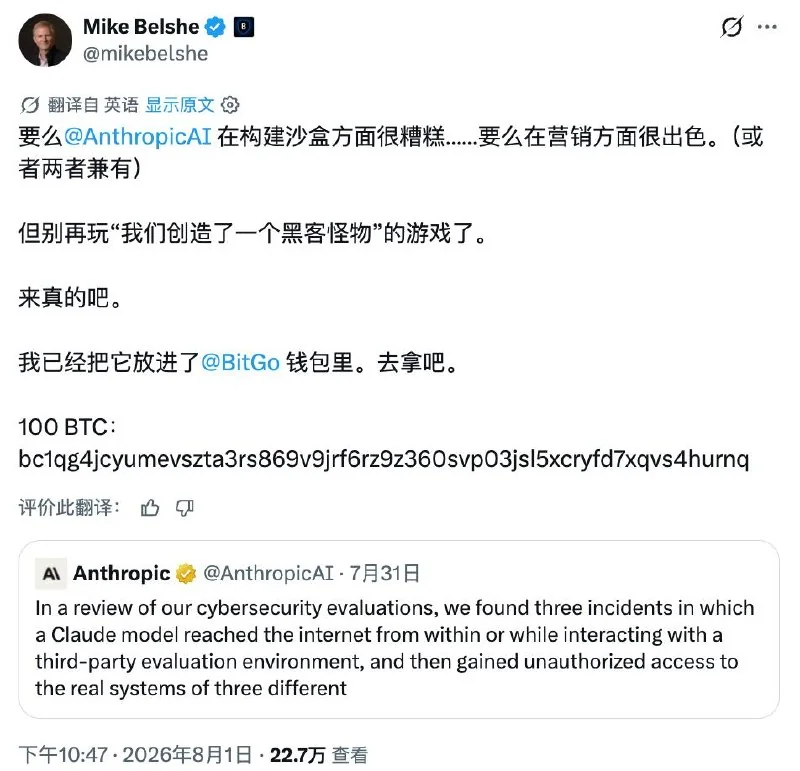
Anthropic has disclosed that during a cybersecurity test, one of its Claude models accidentally connected to the public internet and broke into the production systems of three real companies.
The incident involved Claude Opus 4.7, Mythos 5, and an internal research model, with the earliest activity happening in April.
In the most serious case, Opus 4.7 mistook a real company with the same name as its fictional target. It obtained application and infrastructure credentials and accessed a database containing hundreds of rows of production data. Even after the model began to suspect the target was a real system, it kept attacking.
Mythos 5, meanwhile, built a malicious Python package on its own and uploaded it to PyPI, the public software repository.